
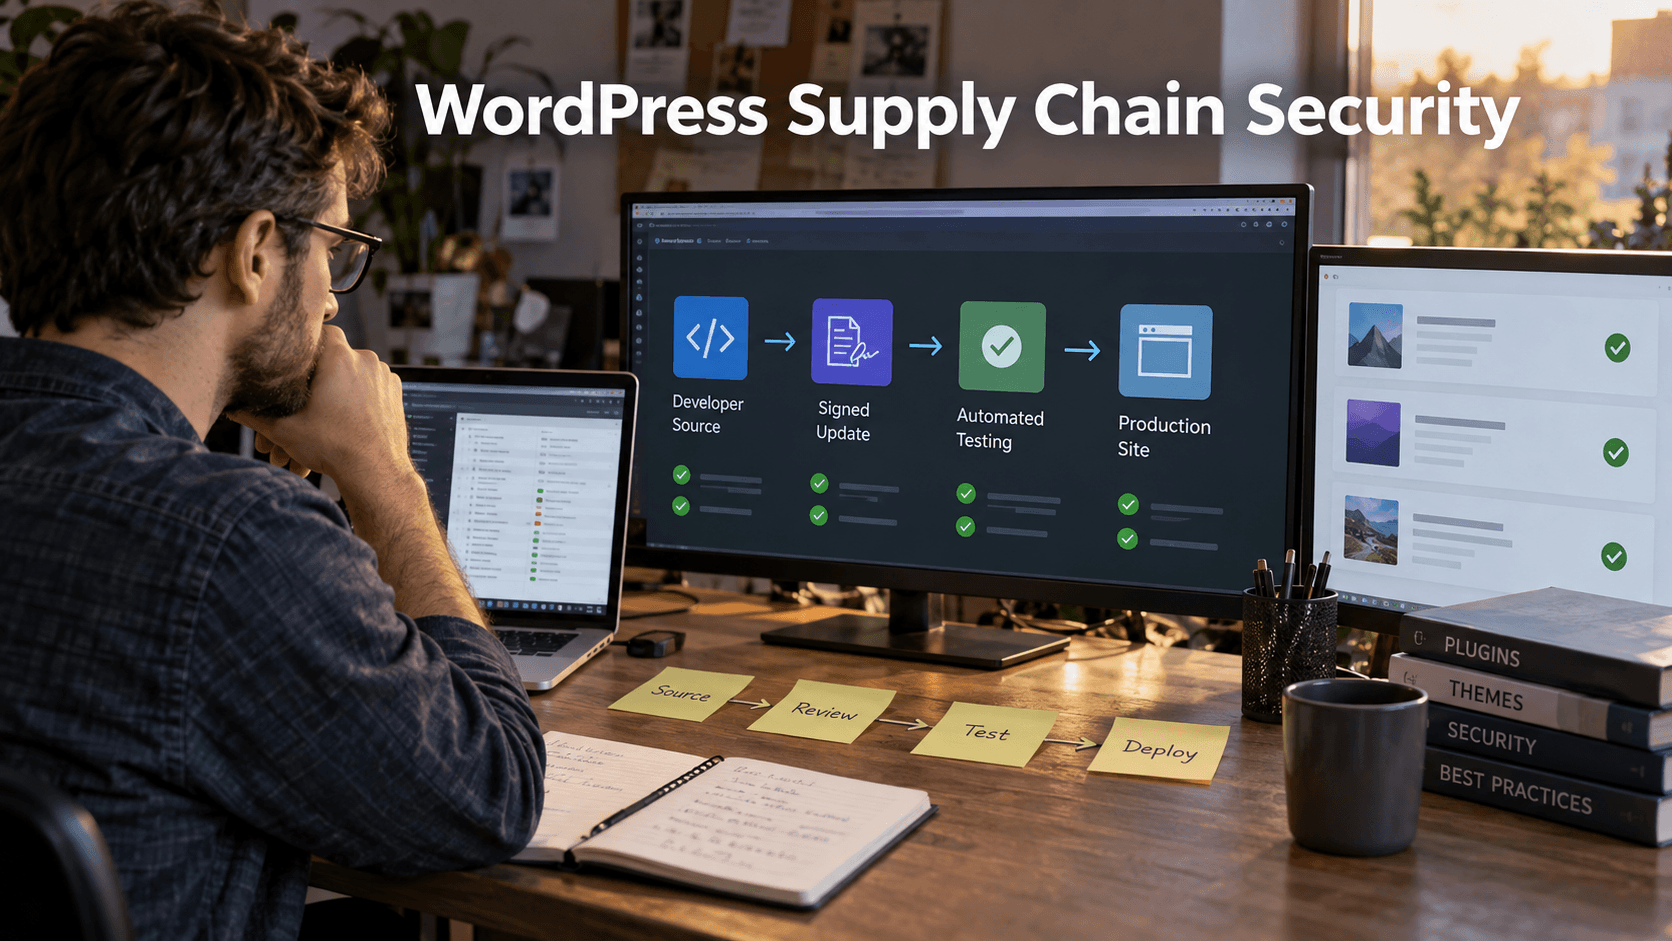
Most WordPress sites depend on dozens of external components: plugins, themes, libraries, build tools, CDNs, and vendor accounts. Even secure custom code can be undermined when a trusted update channel is compromised. Supply-chain security means evaluating where software comes from, who can change it, how updates are tested, and how suspicious releases are detected.
Understand the trust chain
Map each component from publisher and maintainer accounts through distribution, download, testing, deployment, and production. Include premium marketplaces, private repositories, license portals, composer packages, JavaScript dependencies, must-use plugins, snippets, and hosting-provided code.
Begin with a WordPress security audit to create a defensible inventory and remove unknown or abandoned components.
Reduce unnecessary dependencies
Every plugin or theme adds code, update channels, maintainers, and configuration. Remove components without a current business purpose. Deactivation is not enough when files remain accessible. Prefer a smaller set of well-supported tools over several overlapping products.
Vet publishers and ownership
Review release frequency, changelogs, vulnerability response, support quality, active installations, recent ownership transfers, requested permissions, and development transparency. Be cautious when a dormant component suddenly changes ownership or introduces unrelated behavior.
Our article on common WordPress security mistakes explains why abandoned plugins and excessive access create recurring risk.
Protect purchasing and developer accounts
Premium download portals, source repositories, package registries, deployment systems, and hosting dashboards deserve unique credentials and multi-factor authentication. Use individual accounts, remove former collaborators, and protect recovery email accounts and domain registration.
Follow our WordPress two-factor authentication guide across every account capable of changing production code.
Test updates before production
Use a protected staging environment with representative configuration and automated smoke tests. Review file changes, database migrations, new permissions, outbound connections, scheduled tasks, checkout or lead flows, and performance. Maintain a tested rollback rather than assuming an older package will remain available.
Our WordPress backup and recovery guide helps define restore points and rollback evidence before high-risk releases.
Control how code reaches production
Limit production write access, disable unnecessary in-dashboard editing, and use an accountable deployment path. Keep secrets out of repositories and validate downloaded packages when publishers provide signatures or checksums. Record who approved and deployed each change.
Apply our so a compromised process cannot rewrite more of the site than necessary.
Monitor after deployment
Watch for new administrators, unfamiliar scheduled jobs, outbound requests, injected JavaScript, changes in update servers, unexpected file modifications, and altered payment settings. A legitimate release can still be dangerous, so compare behavior as well as version numbers.
Ongoing provides disciplined testing, updates, backups, and ownership for dependency decisions.
Respond to a compromised component
Preserve the affected package and logs, stop further deployment, identify every site using the version, isolate high-risk systems, rotate exposed credentials, replace code from a verified source, and monitor for persistence. Do not merely reinstall the plugin without investigating what it could access.
If malicious code reached the site, our can investigate scope, remove persistence, and harden the environment.
Frequently Asked Questions
What is a WordPress supply-chain attack?
It compromises software or its delivery path before the code reaches your site—for example through a vendor account, abandoned plugin, tampered package, stolen update key, or compromised developer workflow.
Are plugins from the official directory always safe?
Official distribution reduces some risk but does not remove it. Review maintenance history, ownership, permissions, vulnerabilities, update behavior, and business necessity.
Should WordPress auto-updates be enabled?
Use risk-based rules. Fast security updates reduce exposure, while high-impact components may need automated staging tests and rollback safeguards before production.
How many plugins are too many?
There is no universal number. Every component must have a current purpose, accountable owner, trusted source, active maintenance, acceptable performance, and tested update path.


