
Emergency Hacked WordPress Site Recovery
Recover a hacked WordPress site with malware removal, rogue-account review, clean-file restoration, and security hardening. Scope, pricing, and timing follow assessment.
Performance figures, response times, and support examples on this page depend on the project. Final targets, coverage, and acceptance criteria are agreed in writing before work begins.
Redirects to spam sites. A "This site may be hacked" warning in Google. Strange admin accounts you never created. If any of this is happening right now, every hour matters — a hacked site bleeds SEO rankings, customer trust, and revenue until it's cleaned. We recover hacked WordPress sites fast, and we make sure the attackers can't get back in.
What Our Recovery Service Includes
- Complete malware removal — deep scan of core files, themes, plugins, uploads, and the database; every backdoor, injected script, and rogue cron job removed.
- Rogue admin and spam cleanup — attacker-created accounts deleted, injected spam posts and pages purged, database optimized.
- Entry-point identification — we find how they got in (vulnerable plugin, weak credentials, exposed registration) and close that door, so the infection doesn't come back in a week.
- Blacklist and warning removal — Google Search Console review requests and blacklist delisting handled for you.
- Post-recovery hardening — login protection, firewall rules, security headers, file-permission review, and follow-up support defined in the recovery scope.
Proof: A Real Recovery We Delivered
One client came to us with a site under active brute-force attack: attackers had bypassed registration filters, created multiple rogue administrator accounts, and injected over 6,000 spam posts into the database. We quarantined the site, removed every trace of malicious code, purged the spam, masked the login URL, and deployed strict security headers. The site has stayed clean since. Read the full malware removal case study.
Fixed Pricing, Fast Turnaround
Recovery scope, pricing, and estimated timing are agreed after assessment. Access, backups, infection depth, and third-party review queues affect the work. Multisite installations, stores with customer data, and long-standing infections require additional review. Contact us now with your site URL and we'll respond with a free preliminary assessment and your exact quote.
Related services and insights
Continue exploring: the emergency hacked-site recovery guide, signs that a WordPress site is compromised and advanced WordPress security services.
What the service covers
Emergency Malware Removal
Line-by-line file inspection to locate and remove backdoors, webshells, SEO spam injections and obfuscated payloads. We don't rely on automated scanners alone: infected files are verified manually.
Database Decontamination
Rogue admin accounts, spam content injections, and malicious stored procedures are identified and removed. Database table prefixes are randomized to prevent repeat SQL-injection attacks.
Google Blacklist & Search Console Recovery
If Google has flagged your site with a 'This site may be hacked' warning, we submit the cleaned site for review and follow up until the penalty is fully lifted.
Post-Cleanup Hardening
Firewall rules, two-factor authentication, file permission lockdowns, and wp-admin IP whitelisting are deployed to ensure the same attack vector can never be exploited again.
What the work aims to improve
Rapid Incident Triage
Priority TriageWe begin with a rapid assessment of the compromise, access, and hosting constraints, then confirm the recovery scope and expected response window.
Search Visibility Recovery
SEO RemediationWe remove malicious pages and spam, repair compromised files, and support the Search Console review process where a security warning or spam indexation is involved.
Post-Recovery Support
30-Day SupportIf reinfection occurs through the same confirmed entry point within 30 days, we review and remediate that vector at no additional service charge, subject to the agreed recovery scope.
How the work is delivered
Emergency Access & Threat Assessment
We securely receive your hosting and WordPress credentials, lock down the site to prevent further damage, and run a full malware scan across every file and database table.
Surgical Malware Removal
Infected files are cleaned line by line. Backdoor scripts, obfuscated PHP injections, and compromised core files are replaced with verified clean copies from WordPress.org.
Security Hardening & Patch
The original entry vector (outdated plugin, weak password, insecure hosting config) is identified and patched. Firewall rules, 2FA, and file integrity monitoring are deployed.
Verification & Monitoring
The cleaned site is submitted to Google for review. We monitor file integrity and access logs daily for the next 30 days to confirm zero re-infection.
Before we start
- Share the starting point
- Send your website URL, platform, the problem to solve, and any deadline or budget constraints. An existing site may need an assessment before a solution can be recommended.
- Agree what is included
- Confirm deliverables, exclusions, dependencies, and pricing before work begins. Hosting, paid tools, content entry, and ongoing support should be discussed separately when needed.
- Define acceptance checks
- Agree which pages, devices, integrations, and measurements will be checked. Compare results with a documented baseline where performance or search work is involved.
- Plan access and handover
- Discuss account ownership, the access needed for delivery, documentation, and any training or maintenance arrangements. Confirm ongoing support in the written scope.
Please do not send passwords, API keys, or customer records through the inquiry form or chat.
Frequently Asked Questions
How did my WordPress site get hacked?
The most common entry points are outdated plugins with known vulnerabilities, weak admin passwords, and insecure hosting configurations. During our cleanup, we identify the exact exploit used and patch it.
Will I lose any of my content or media files?
We take a full backup before cleanup starts, then remove only the malicious code and files, leaving your legitimate content, images and database records in place. The exception is data the attacker had already deleted before we arrived, which cleanup cannot bring back unless a clean backup exists.
How long does recovery take?
Recovery time depends on the infection, hosting access, database contamination, and whether the site is still under attack. We provide an initial assessment and expected window before cleanup, then share progress updates as work proceeds.
How much does hacked WordPress site recovery cost?
We quote a fixed price after a free preliminary assessment, so you know the total before we start. Pricing scales with infection scope: number of compromised files, database contamination, and whether the site is under active attack. We do not bill hourly for emergency work, because nobody in a crisis should be watching a meter run.
Can't I just restore my hacked site from a backup?
Usually not, and it's often actively harmful. Infections commonly sit dormant for weeks before activating, meaning your backups may already be infected. Restoring also does nothing about the vulnerability that let attackers in, so reinfection follows within days. And it won't clear a Google blacklisting, which requires a reconsideration request regardless of what you restore.
How do I get the 'This site may be hacked' warning removed from Google?
The warning is lifted through a reconsideration request in Google Search Console after the site is demonstrably clean. Review timing is controlled by Google, so we cannot guarantee a fixed turnaround. We verify the property, document the remediation, submit the request, and address malicious URLs indexed under your domain.
My host suspended my account for malware. Can you still help?
Yes, this is common. Hosts suspend to stop outbound spam or malware distribution and generally restore access for remediation when a professional is engaged. We can liaise with your host's abuse team directly, or work from a local copy and hand back a verified-clean codebase along with the remediation documentation hosts require.
Will my site get hacked again after you clean it?
Recovery includes tracing and closing the confirmed entry point, rotating credentials, and applying suitable hardening. No provider can promise that a site will never be compromised through a different vulnerability. If reinfection occurs through the same confirmed vector within 30 days, we review it under the agreed recovery scope.
Explore published projects
View All Projects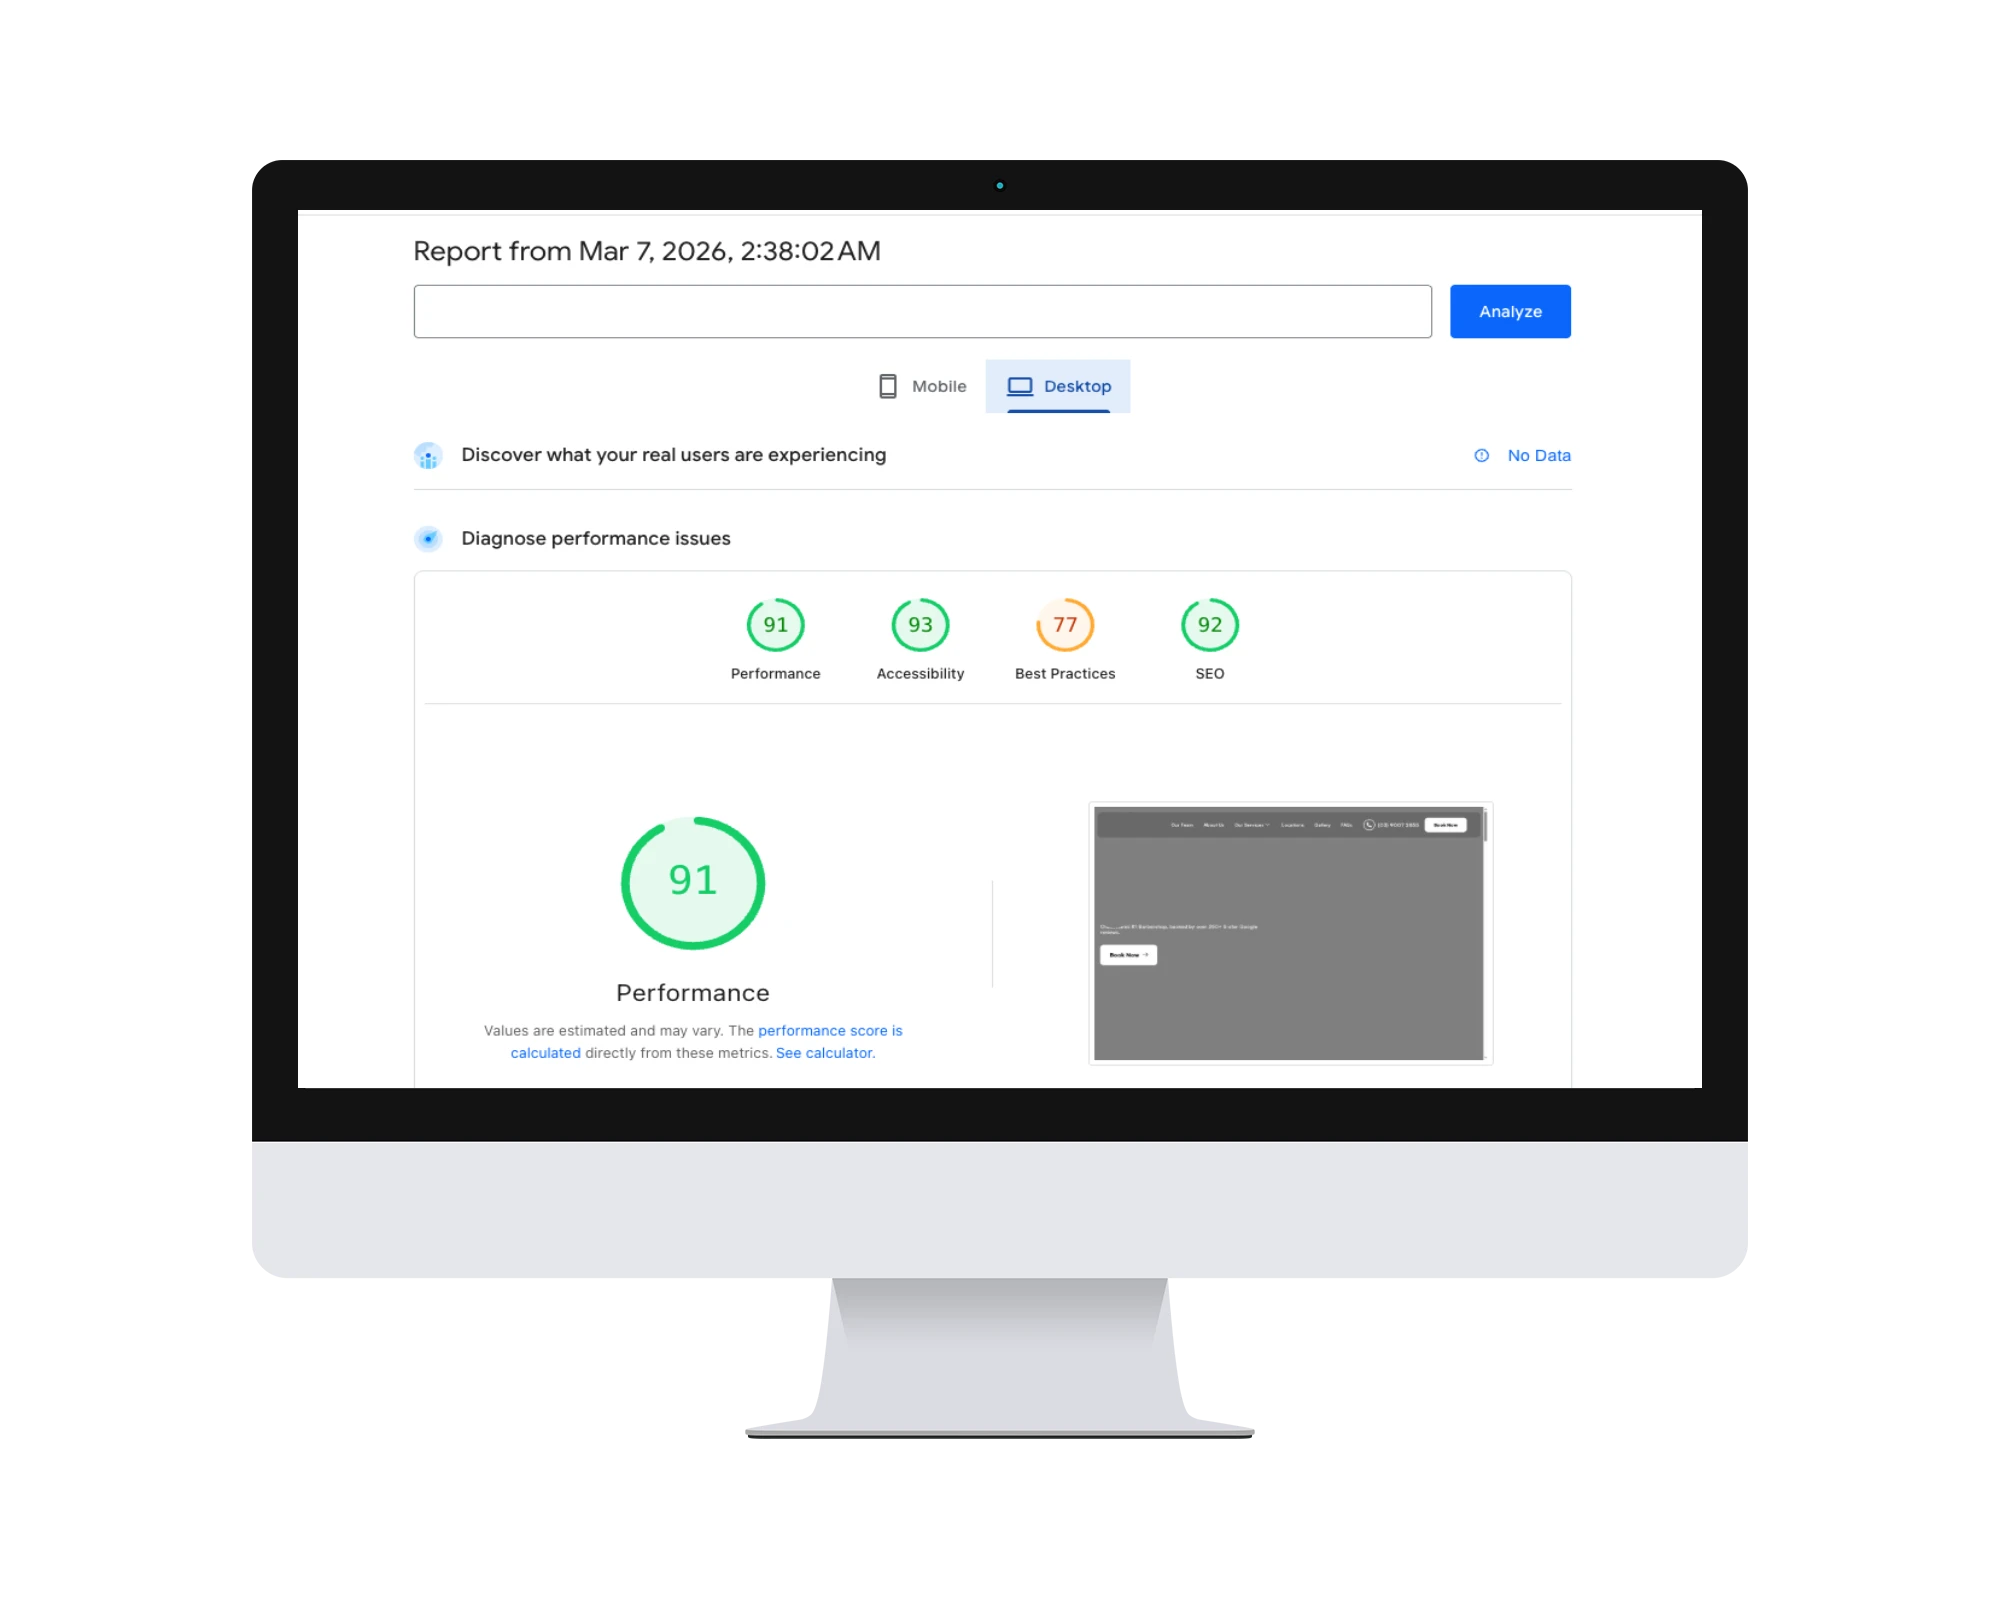
WordPress Speed Optimization: Rescuing a Sub-20 Desktop Score
Premier Solutions rescued a WordPress site failing desktop speed tests (under 20/100) using next-gen WebP images, multi-tiered caching, and JS minification to deliver top-tier Core Web Vitals.
View Case Study
WordPress Security Recovery: Complete Malware Removal & Hardening
A WordPress malware-recovery case study covering spam removal, rogue administrators, clean-file restoration and post-cleanup hardening.
View Case Study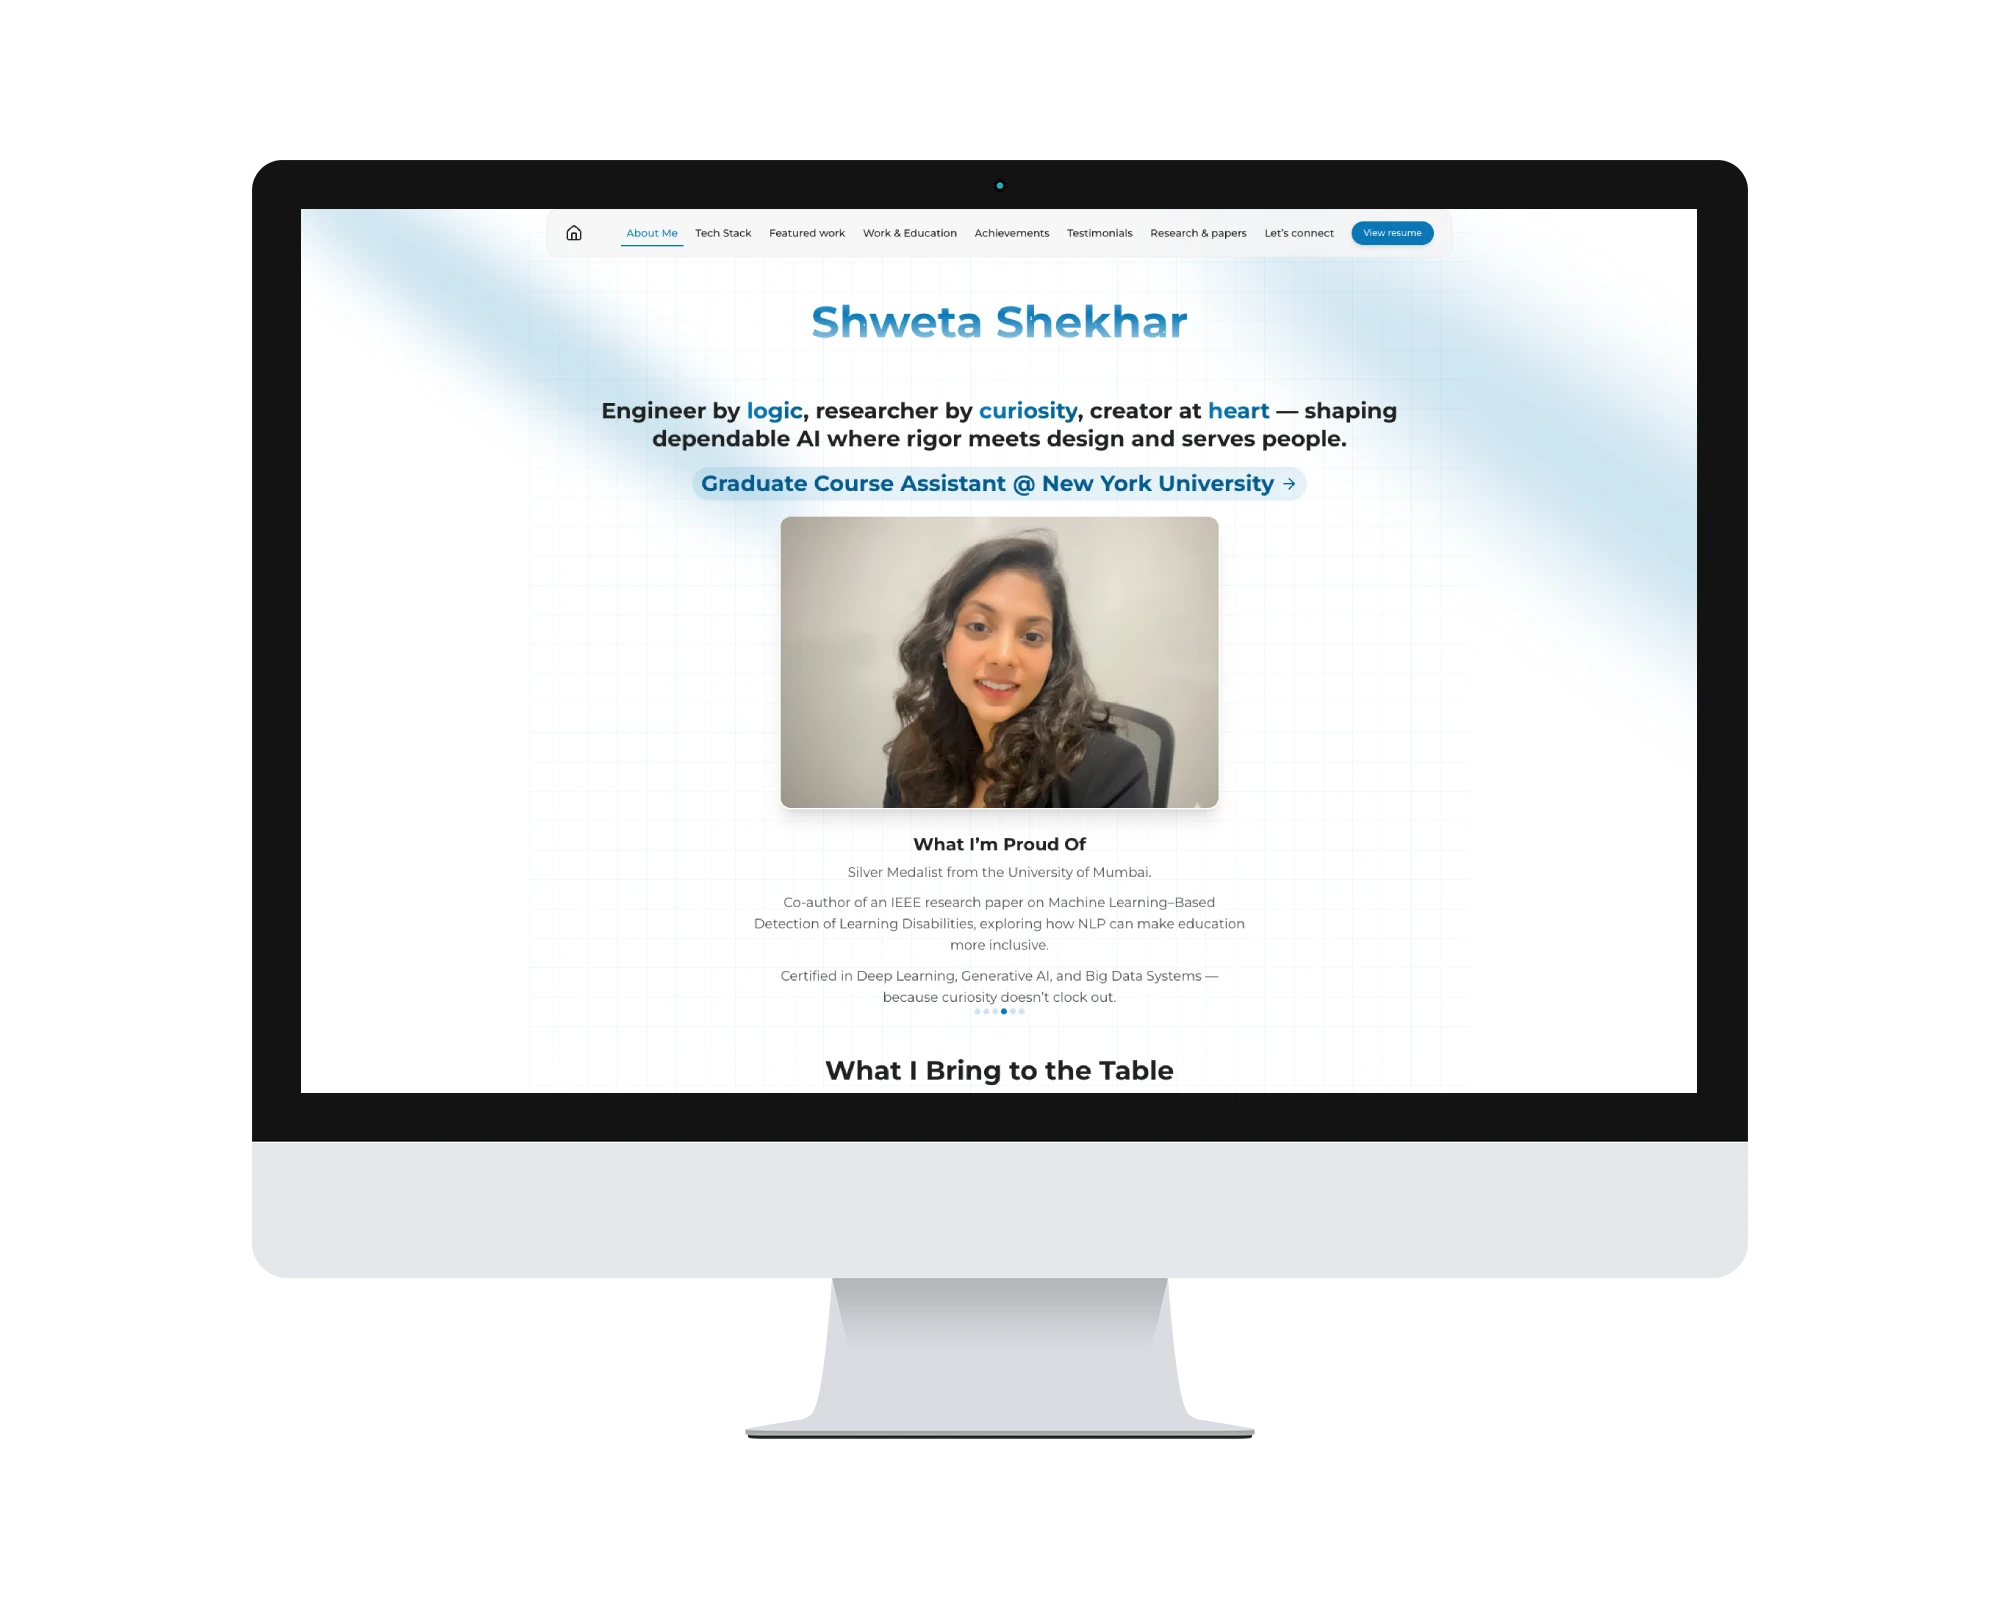
High-Performance Single-Page Portfolio: Next.js & React.js Development
Premier Solutions engineered a fast, single-page personal portfolio with Next.js and React.js — a responsive, highly optimized digital presence with an app-like experience.
View Case StudyExplore our services

AI Search Optimization (AEO & GEO)
Improve how search and AI answer engines understand your website through crawlability, clear content, relevant structured data, and consistent business information.
Learn More
AI Integration & Chatbot Development
Connect Claude, ChatGPT, or Gemini to your website. We build custom AI chatbots, RAG knowledge systems, MCP integrations, and AI-powered workflows for WordPress and Next.js platforms.
Learn More
WordPress Maintenance & Care Plans
Monthly WordPress maintenance with tested updates, security monitoring, daily backups, uptime checks and priority support.
Learn More