
Advanced WordPress Security Solutions
WordPress security audits, hardening, malware removal, managed updates, and scoped monitoring. Published recovery case studies show the work performed on individual sites.
Performance figures, response times, and support examples on this page depend on the project. Final targets, coverage, and acceptance criteria are agreed in writing before work begins.
WordPress powers over 40% of the web, which makes it the number-one target for automated attacks. A basic security plugin isn't enough — modern attackers use sophisticated techniques to bypass standard defenses, inject malware, and quietly compromise your site for weeks before you notice. The cost of a breach isn't just a repair bill; it's lost customer trust, destroyed SEO rankings, and revenue that doesn't come back. Our WordPress security services prevent that from happening, and fix it fast when it already has.
What We Do
- Security audits and hardening — deep-dive analysis of your core files, themes, plugins, and server configuration. We close vulnerabilities before they're exploited: security headers (XSS, clickjacking protection), custom login paths, file permission lockdowns, database hardening, and Web Application Firewall deployment.
- Malware removal and hack recovery — if your site is already compromised, our emergency hacked-site recovery service cleans the infection, removes backdoors, purges spam, and identifies exactly how the attackers got in.
- Managed updates — outdated plugins are the #1 attack vector. We apply core, theme, and plugin updates on a schedule, tested in staging first, so nothing breaks your live site. This is also included in every WordPress maintenance plan.
- Monitoring and alerts with coverage defined in the support agreement — real-time malware scanning, uptime monitoring, and file-integrity checks. If something changes that shouldn't, we know immediately.
- Blacklist removal — if Google or antivirus providers have flagged your site, we handle the review requests and delisting process to restore your reputation.
Proof: A Real Recovery We Delivered
A client came to us with a WordPress site under active brute-force attack. Attackers had created multiple rogue admin accounts and injected over 6,000 spam posts into the database. We quarantined the site, removed every trace of malicious code, purged the spam, masked the login URL, and deployed strict security headers. The site has stayed clean since. Read the full malware removal case study.
Not sure if your site is secure? Our guide covers the 12 warning signs your WordPress site has been hacked, and for firewall configuration advice, see our Wordfence vs Cloudflare comparison.
Security Benchmarks
- Automated zero-day hardening — virtual patching applied at the firewall within hours of public CVE disclosure, protecting you before a plugin author ships a fix.
- Under 60-minute detection-to-alert on file integrity events.
- Zero known-vulnerable components in production, verified continuously against CVE feeds.
- A+ rating on Mozilla Observatory and Qualys SSL Labs.
What the service covers
Web Application Firewall (WAF) Deployment
Application-layer firewall rules that block SQL injection, cross-site scripting (XSS), and brute-force login attacks before they reach your WordPress installation.
File Integrity Monitoring
Automated daily comparison of every WordPress core, theme, and plugin file against known-clean checksums. Any unauthorized modification triggers an instant alert.
Vulnerability Assessment & Patching
Continuous CVE database monitoring for every plugin and theme in your stack. Critical vulnerabilities are patched or mitigated within 24 hours of public disclosure.
Access Control & Authentication Hardening
Two-factor authentication enforcement, IP-restricted wp-admin access, disabled XML-RPC, session timeout policies, and strong password requirements for all user roles.
What the work aims to improve
Prevent Breaches Before They Happen
Proactive DefenseReactive security is expensive. Our proactive approach — vulnerability scanning, firewall rules, and file integrity monitoring — stops attacks at the perimeter, not after they've succeeded.
Protect Your SEO Investment
SEO SafeMalware infections trigger Google's Safe Browsing warnings, causing immediate ranking drops and visitor loss. Our security layer ensures your organic search equity stays protected.
Security Standards Alignment
OWASP-AlignedWe apply practical hardening controls informed by OWASP guidance. Where formal compliance is required, controls must be assessed against your full environment and obligations.
How the work is delivered
Comprehensive Security Audit
Full assessment of your hosting environment, WordPress configuration, installed plugins, user roles, file permissions, and SSL/TLS configuration.
Vulnerability Remediation
Identified vulnerabilities are patched, insecure plugins are replaced with secure alternatives, and server configurations are hardened according to CIS WordPress benchmarks.
Firewall & Monitoring Deployment
WAF rules are configured for your specific traffic patterns, file integrity monitoring is activated, and automated backup schedules are validated.
Ongoing Security Operations
Continuous CVE monitoring, monthly security reports, incident response SLA, and quarterly penetration testing against your WordPress installation.
Before we start
- Share the starting point
- Send your website URL, platform, the problem to solve, and any deadline or budget constraints. An existing site may need an assessment before a solution can be recommended.
- Agree what is included
- Confirm deliverables, exclusions, dependencies, and pricing before work begins. Hosting, paid tools, content entry, and ongoing support should be discussed separately when needed.
- Define acceptance checks
- Agree which pages, devices, integrations, and measurements will be checked. Compare results with a documented baseline where performance or search work is involved.
- Plan access and handover
- Discuss account ownership, the access needed for delivery, documentation, and any training or maintenance arrangements. Confirm ongoing support in the written scope.
Please do not send passwords, API keys, or customer records through the inquiry form or chat.
Frequently Asked Questions
Is WordPress really secure enough for business-critical websites?
WordPress core is well-maintained and regularly patched. The vast majority of WordPress security incidents are caused by outdated plugins, weak passwords, and misconfigured hosting — all of which are addressed by our hardening service.
Do I need a security plugin like Wordfence or Sucuri?
Wordfence or Sucuri can provide useful endpoint controls. Whether you need one depends on your hosting, Cloudflare or server-level WAF coverage, monitoring, and performance requirements. We review the stack and keep the controls that add meaningful coverage.
What does 'automated zero-day hardening' actually mean?
Virtual patching means adding a targeted firewall rule when a known exploit is being actively abused and an upstream fix is not yet available or deployed. Availability and response time depend on the vulnerability, hosting stack, and rule coverage; it complements, rather than replaces, vendor updates.
How quickly can you respond if my site is actively under attack?
Response time depends on the support plan, access, hosting provider, and severity of the incident. Monitoring clients are alerted according to their plan, while emergency recovery work is triaged as quickly as capacity and access allow. We confirm the response window before work begins.
Does hardening my site affect its speed?
Well-designed hardening should have minimal performance impact, but every control adds some processing or operational overhead. We choose the lightest effective layer, test changes, and remove redundant controls where appropriate.
How much do WordPress security services cost?
A one-time audit and hardening pass typically starts in the low four figures depending on site complexity. Ongoing monitoring and managed security is offered as a monthly plan, priced by site count and traffic. We quote a fixed price after reviewing your current setup — no hourly billing.
Explore published projects
View All Projects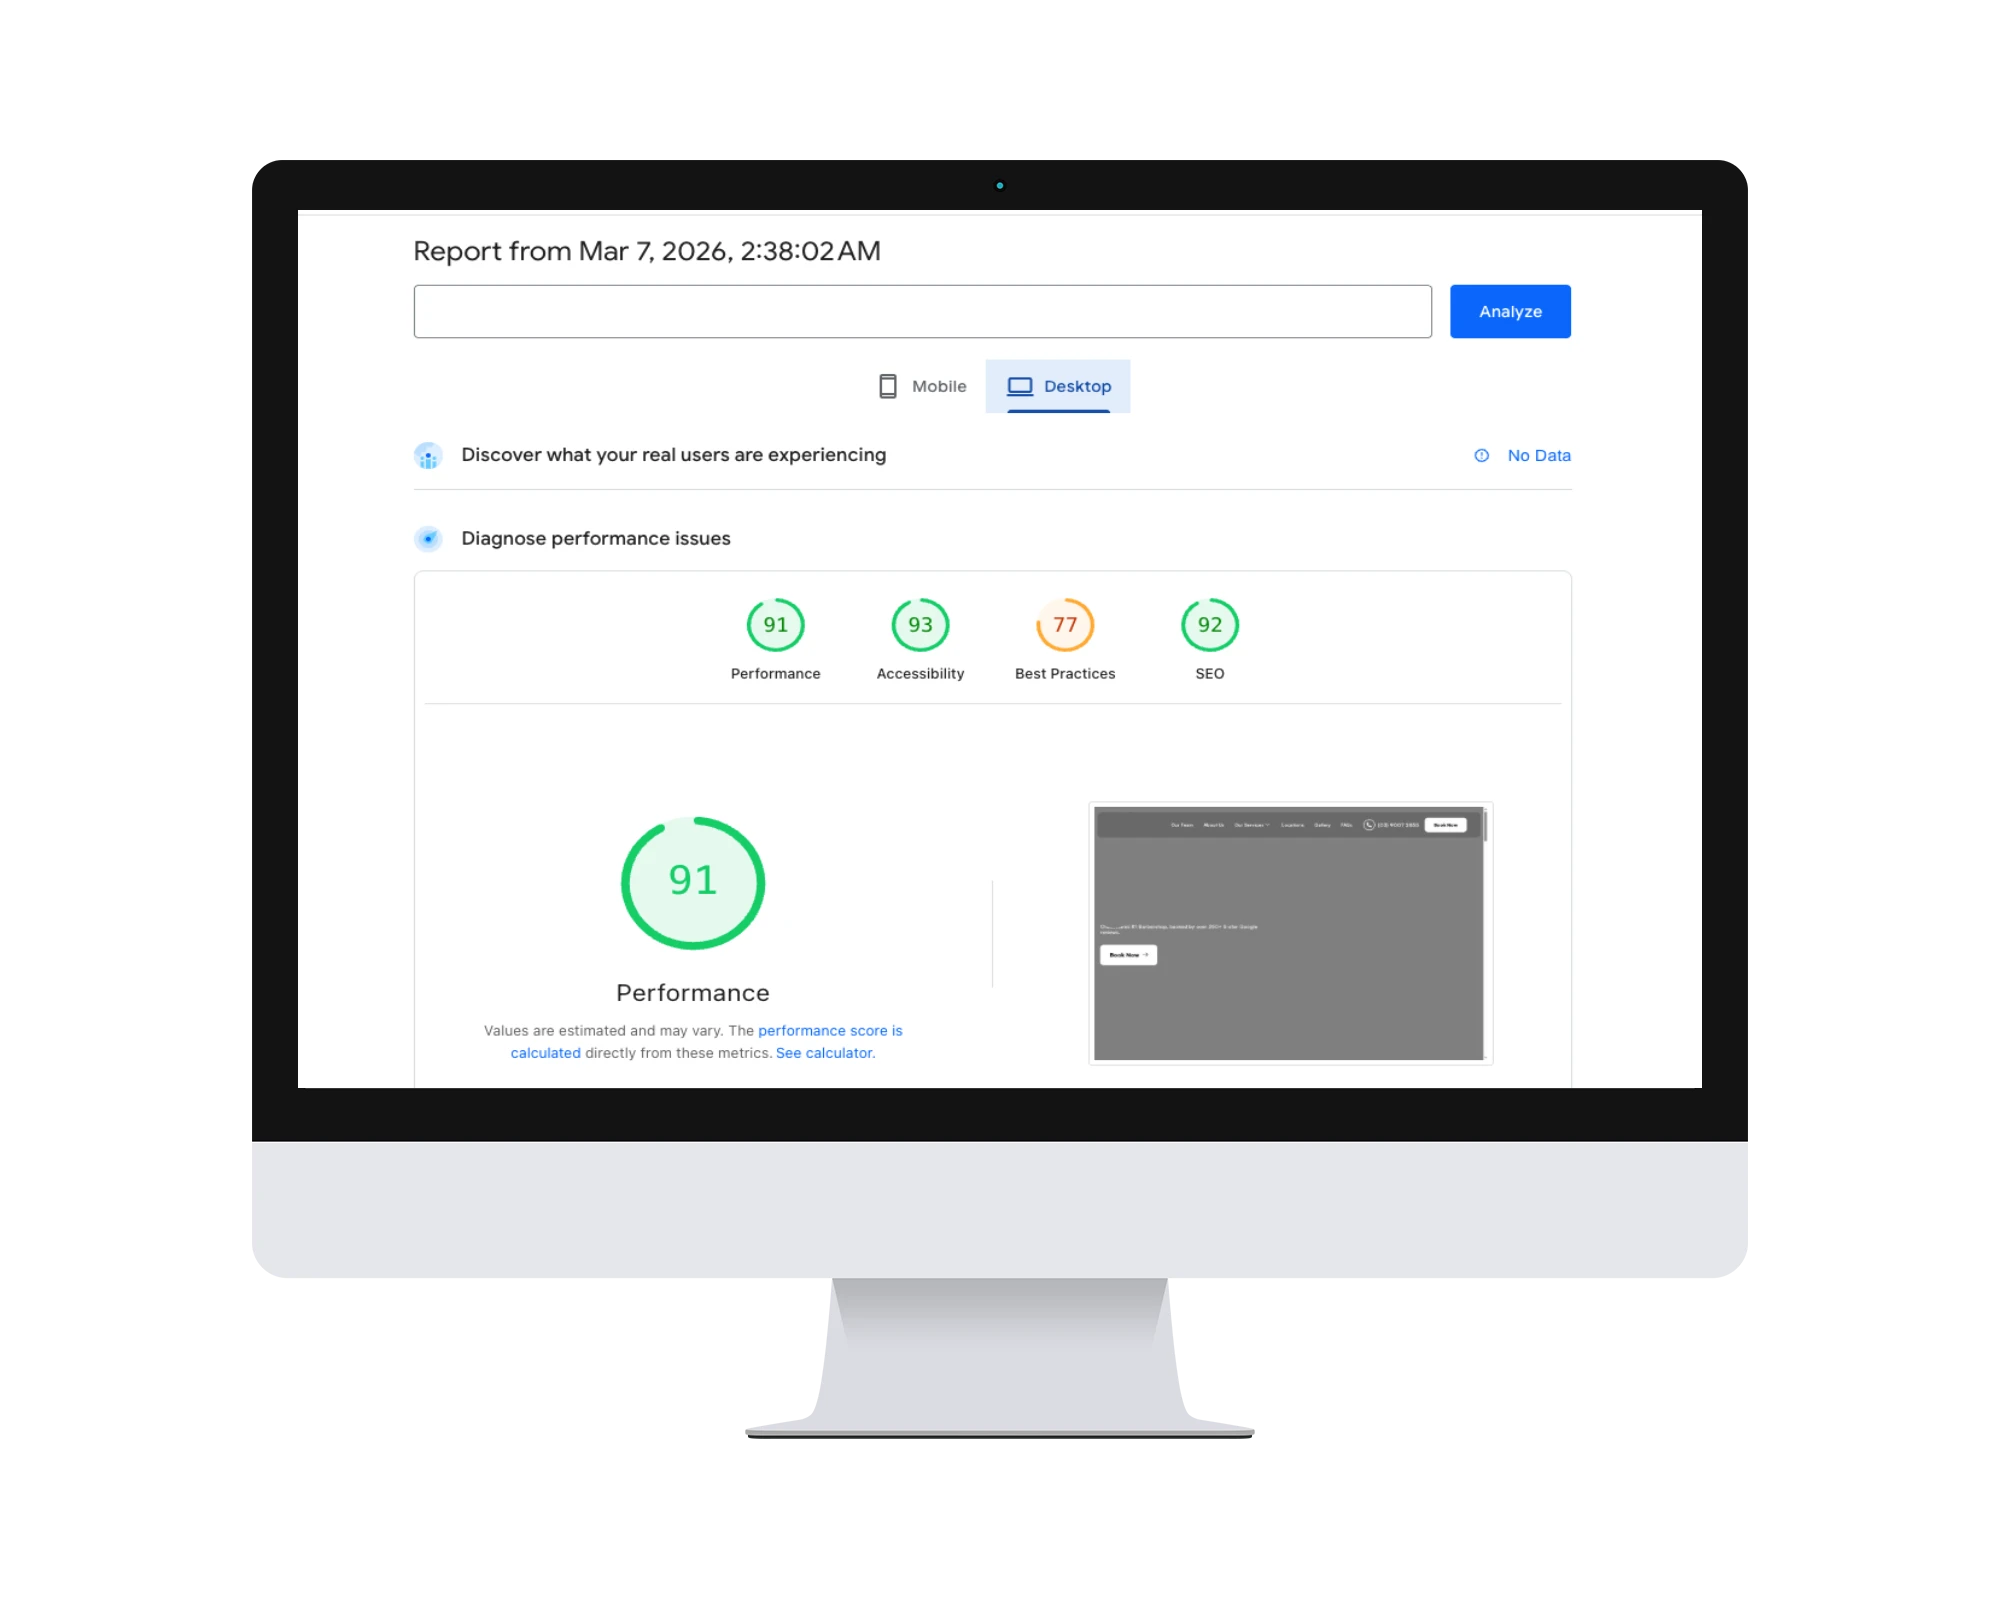
WordPress Speed Optimization: Rescuing a Sub-20 Desktop Score
Premier Solutions rescued a WordPress site failing desktop speed tests (under 20/100) using next-gen WebP images, multi-tiered caching, and JS minification to deliver top-tier Core Web Vitals.
View Case Study
WordPress Security Recovery: Complete Malware Removal & Hardening
A WordPress malware-recovery case study covering spam removal, rogue administrators, clean-file restoration and post-cleanup hardening.
View Case Study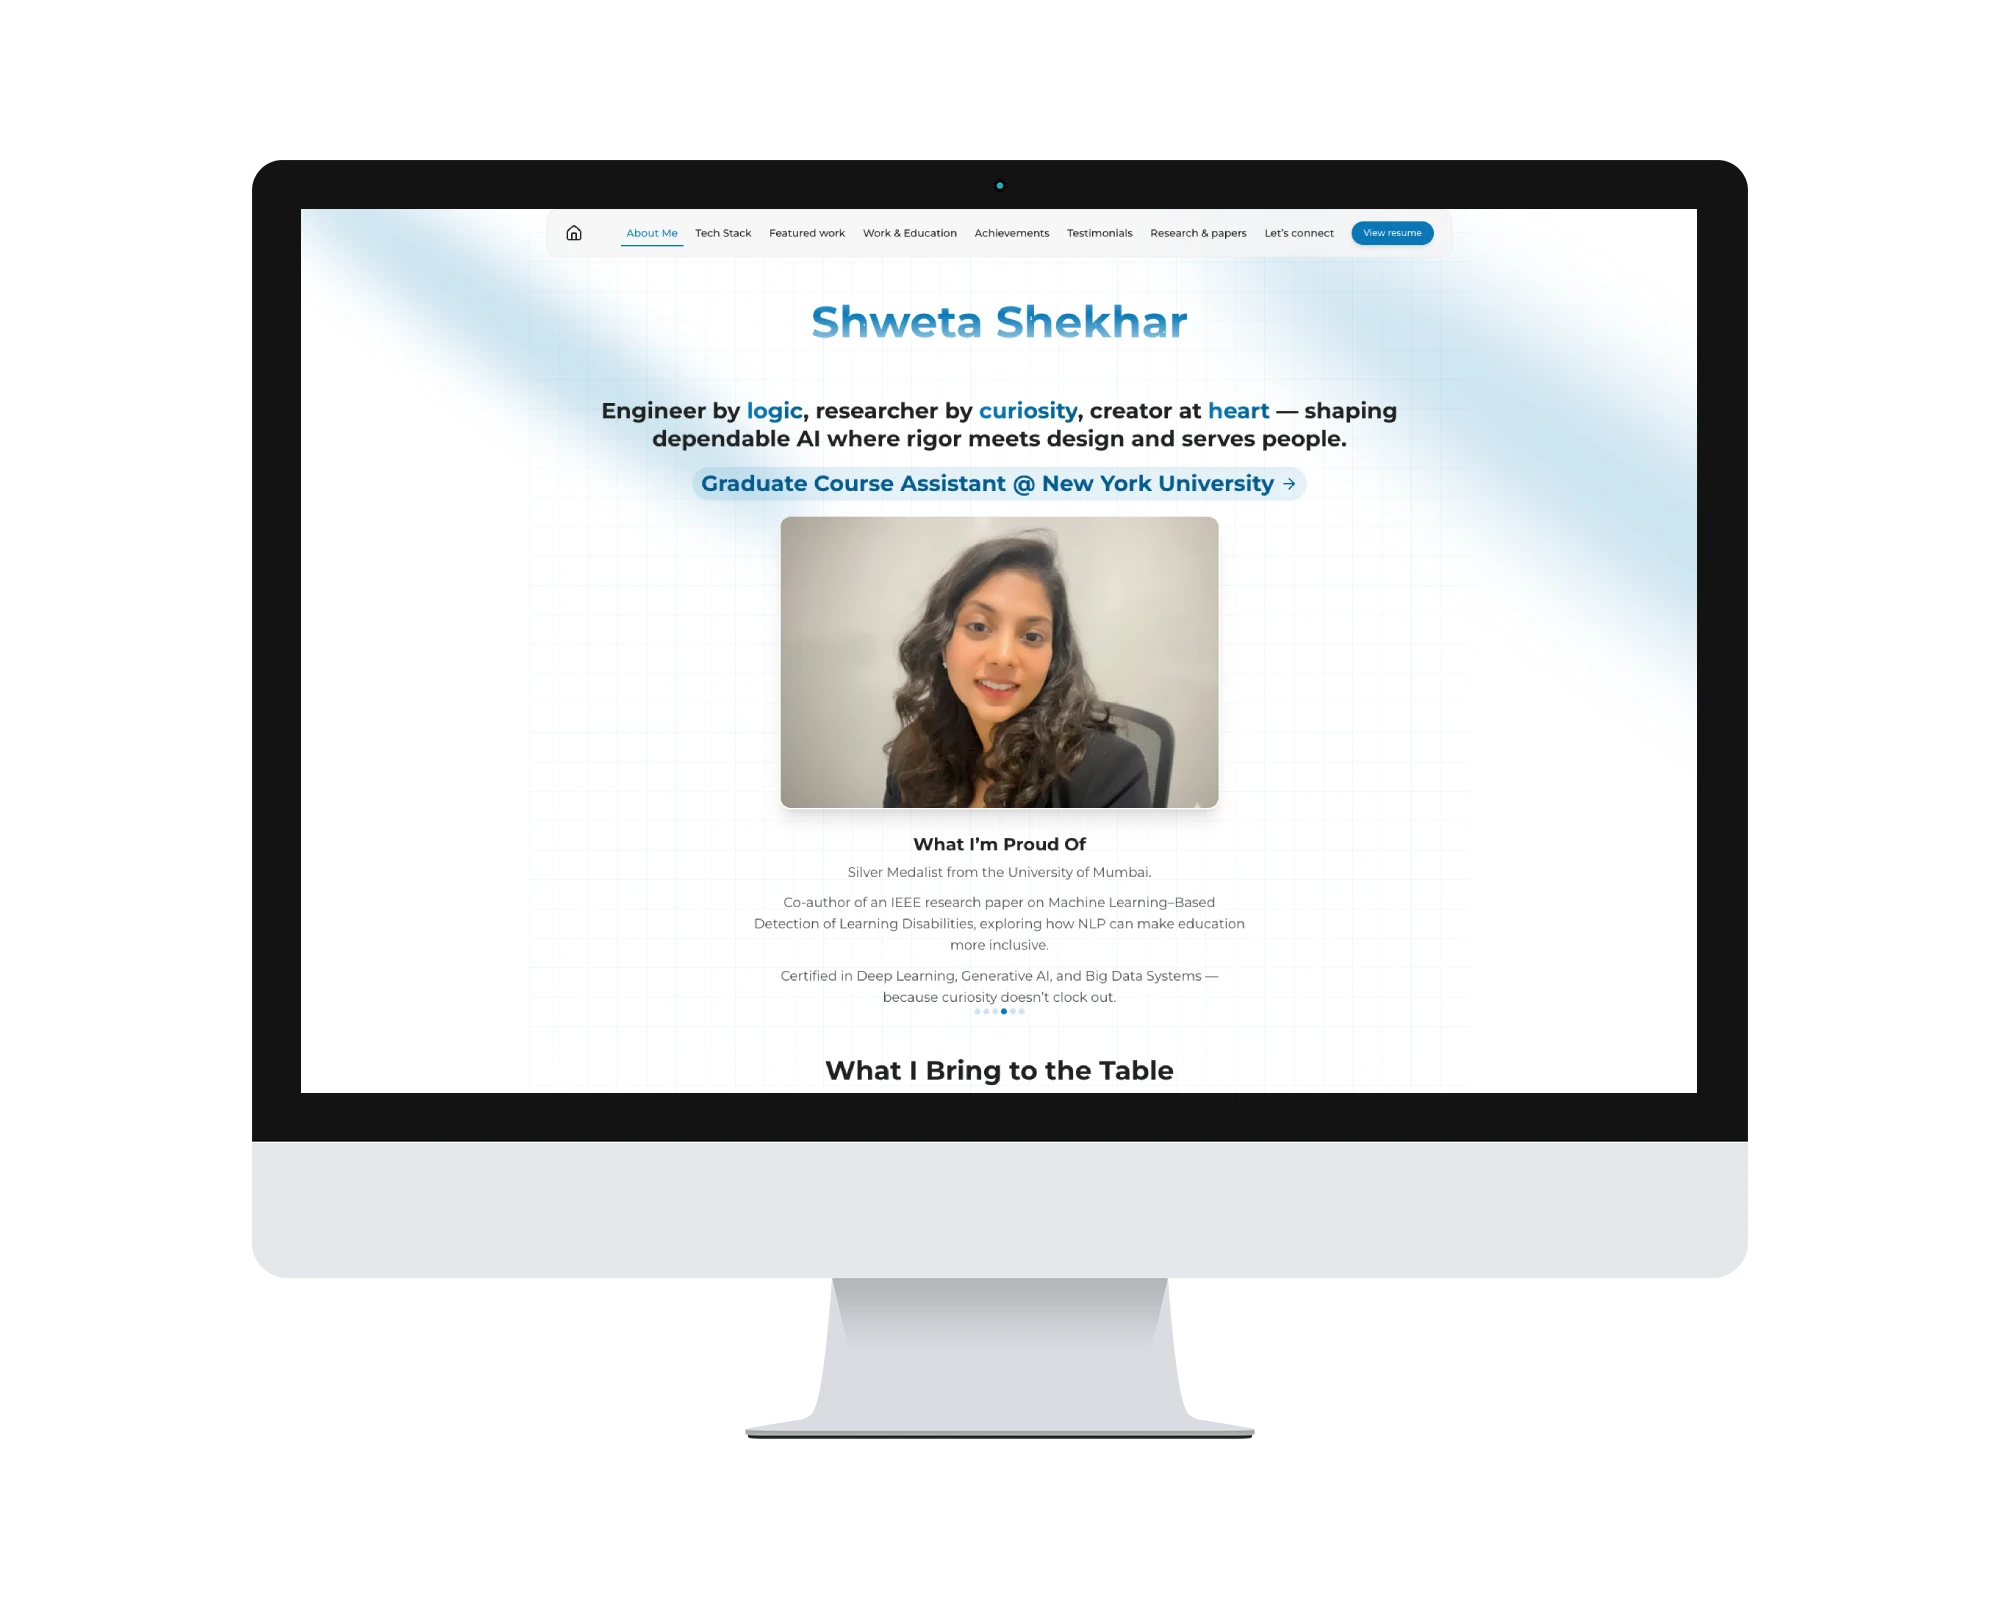
High-Performance Single-Page Portfolio: Next.js & React.js Development
Premier Solutions engineered a fast, single-page personal portfolio with Next.js and React.js — a responsive, highly optimized digital presence with an app-like experience.
View Case StudyExplore our services

AI Search Optimization (AEO & GEO)
Improve how search and AI answer engines understand your website through crawlability, clear content, relevant structured data, and consistent business information.
Learn More
AI Integration & Chatbot Development
Connect Claude, ChatGPT, or Gemini to your website. We build custom AI chatbots, RAG knowledge systems, MCP integrations, and AI-powered workflows for WordPress and Next.js platforms.
Learn More
WordPress Maintenance & Care Plans
Monthly WordPress maintenance with tested updates, security monitoring, daily backups, uptime checks and priority support.
Learn More