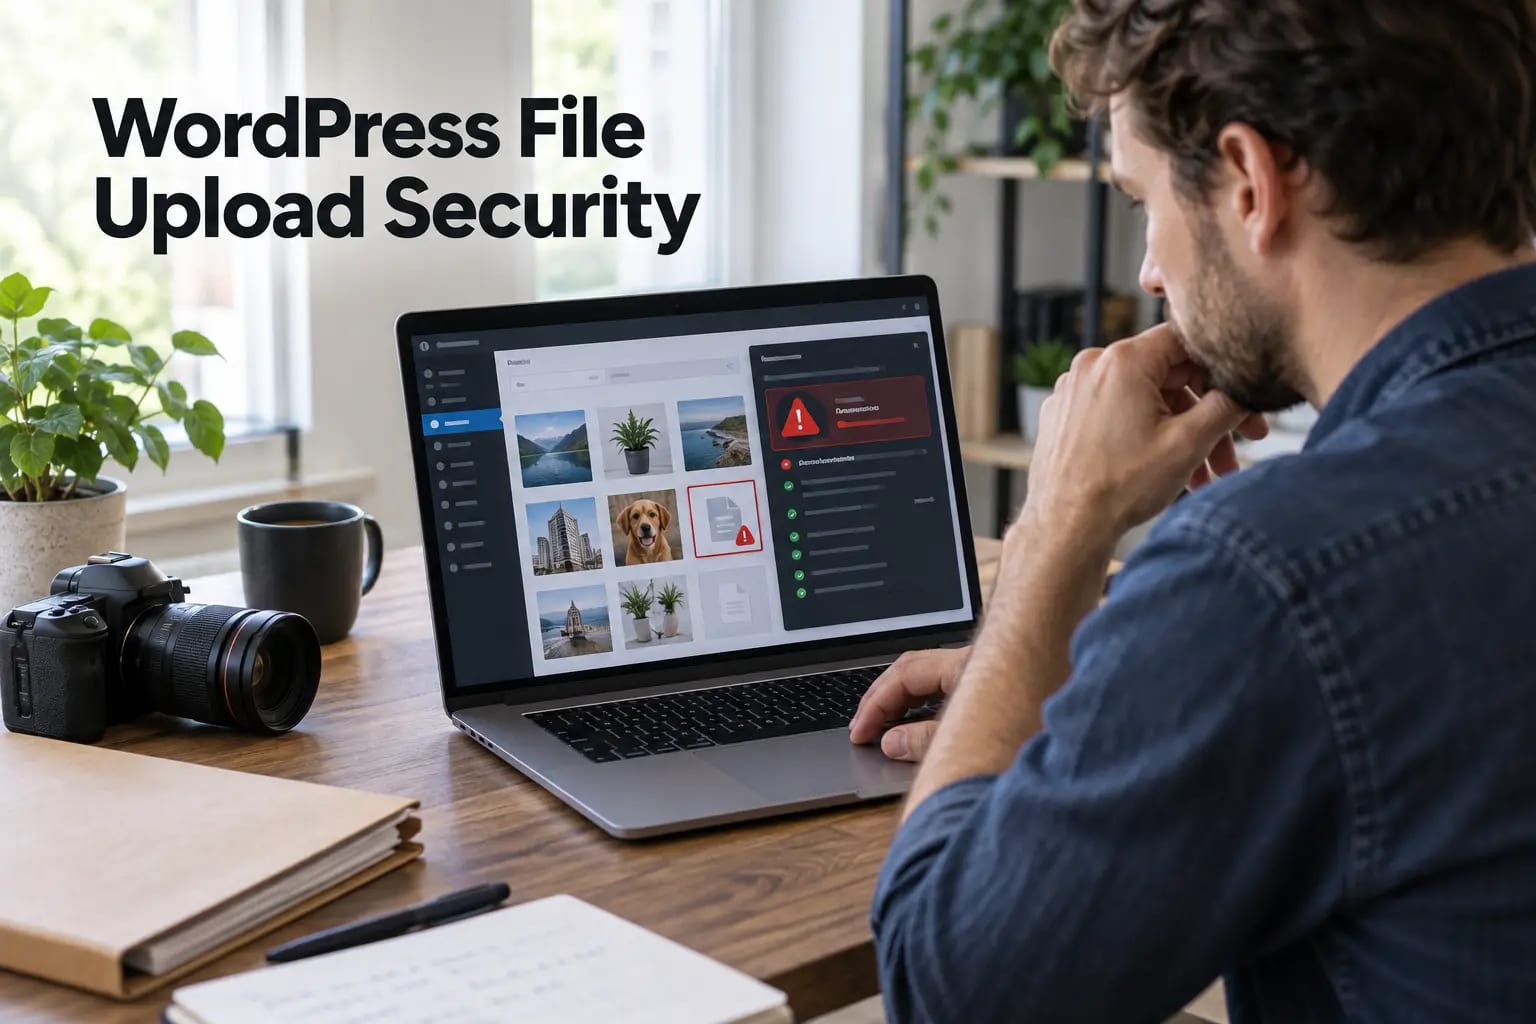
File uploads turn a WordPress site from a publishing system into a file-processing service. Media libraries, contact forms, job applications, support portals and membership features may all accept data from a user’s device. If validation or storage is weak, an upload can become malware, stored cross-site scripting, sensitive-data exposure or a path to remote code execution.
A secure design assumes that the filename, extension, browser-reported MIME type and file contents can disagree. It limits what is accepted, validates again on the server and stores files so they cannot execute as application code.
1. Decide which files the business actually needs
Start with an allowlist, not a blocklist. If a form only needs PDF résumés and common image formats, do not accept archives, scripts, office macros or arbitrary files. WordPress already maintains allowed MIME types, and extensions should be added only after their risks and handling requirements are understood.
- List the exact file extensions and content types required for each upload field.
- Set a per-file size limit and a per-user or per-IP submission limit.
- Reject double extensions, control characters and deceptive filenames.
- Do not enable unrestricted uploads as a shortcut.
Make sure upload directories also follow the ownership and access guidance in our WordPress file permissions guide. Validation cannot compensate for a directory that allows uploaded code to run.
2. Validate on the server
Browser checks improve user experience but are not a security boundary. Validate the extension, detected MIME type and file signature after the server receives the file. Use WordPress upload APIs rather than bypassing their built-in checks. Rename files to a generated value and avoid reflecting the original filename directly into HTML.
Images deserve special care. Re-encoding a supported raster image can remove unexpected metadata and invalid structures, but it should happen in a controlled library with resource limits. SVG is active XML content, not a simple bitmap; accept it only with a robust sanitizer and a clear need.
3. Separate uploaded content from executable code
Configure the web server so upload directories cannot execute PHP or other scripts. Where possible, store private documents outside the public web root or in object storage and deliver them through authorized, time-limited requests. A hard-to-guess URL is not access control.
Review these boundaries during a recurring WordPress security audit and test both direct file URLs and application-level permissions.
4. Protect form and membership uploads
Authenticate users when the workflow requires an account, verify nonces for browser requests and enforce authorization for every download. Rate-limit anonymous forms, add anti-automation controls and prevent one account from exhausting storage. Keep uploaded identity documents and support attachments out of the normal public media library.
Define a retention period. Files that are no longer needed increase privacy and breach impact. Deletion should remove derivatives, thumbnails, temporary chunks and external storage copies according to the same policy.
Put these ideas to work.
From a specific fix to a complete website, we can help you define the scope and get it done.
Discuss my websiteWeb DesignShare your goals. We typically reply within 4 hours with questions and practical next steps.
5. Scan files without creating false confidence
Malware scanning is a useful additional layer, not a substitute for validation and non-executable storage. Quarantine suspicious files before they reach users, fail safely when the scanning service is unavailable and record the decision without logging sensitive file contents.
If scanning finds a web shell or unexpected executable, follow the hacked WordPress recovery service process: preserve evidence, isolate the site, identify the entry point and remove persistence before restoring service.
6. Monitor upload behavior
Alert on blocked executable types, sudden volume increases, repeated failures, unusual file sizes and uploads followed by file changes or new administrators. Logs should capture the authenticated account, source, result, detected type and storage destination while minimizing personal data.
Correlate upload events with the file-integrity and login signals in the WordPress security monitoring guide to distinguish a user mistake from an active intrusion.
Upload-security checklist
- Every upload field has a narrow extension and MIME allowlist.
- Server-side validation checks content, not only the filename.
- Uploaded files cannot execute in their storage directory.
- Private files require authorization on every request.
- Rate, count, dimensions and size are limited.
- Malware scanning, quarantine and failure behavior are tested.
- Retention and deletion include derived and external copies.
For ongoing protection, combine this checklist with WordPress security maintenance so plugin updates, logs, permissions and storage controls are reviewed together.
Final takeaway
Secure uploads require several independent barriers: a narrow business requirement, strict server-side validation, non-executable storage, authorization, limits, scanning and monitoring. Design the workflow so a missed signature or scanner failure does not turn an uploaded file into executable code.
Frequently asked questions
Is checking the file extension enough for WordPress uploads?
No. Extensions are easy to rename. Validate the detected content type and file structure on the server, then store the file where it cannot execute.
Is it safe to allow SVG uploads in WordPress?
SVG can contain active content. Allow it only when required, sanitize it with a maintained solution and deliver it with appropriate content and security controls.
Should uploaded files be stored in the Media Library?
Public editorial images often belong there. Private documents, identity files and support attachments usually need separate storage with authorization and retention controls.
Does malware scanning make uploads safe?
Scanning adds defense in depth but cannot detect every threat. Keep strict allowlists, validation, safe storage, permissions, limits and monitoring.