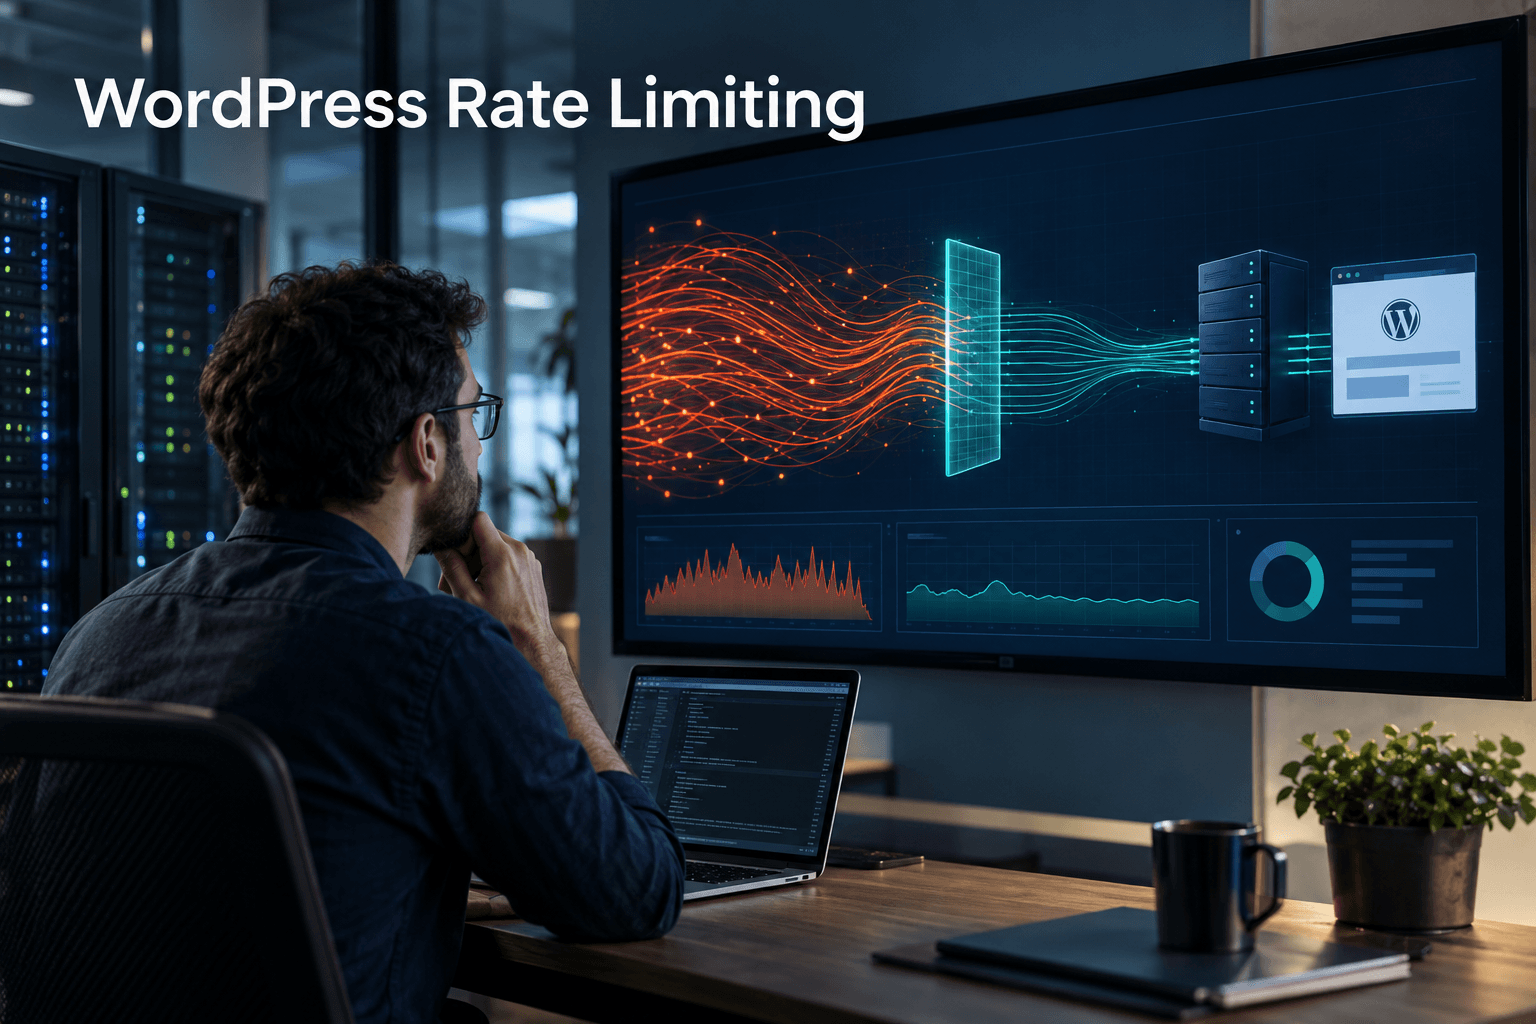
Rate limiting is one of the most practical ways to protect a WordPress site from automated abuse. It controls how quickly a client can repeat a sensitive action, helping the site absorb password guessing, API scraping, form spam and checkout automation without treating every visitor as hostile.
The goal is not to impose one arbitrary number across the whole website. A useful policy reflects the action being protected, the normal traffic pattern and the cost of a false positive. Ten rapid product searches, for example, should not be judged like ten failed administrator logins.
Where abusive traffic reaches WordPress
Start with an endpoint inventory. Common targets include /wp-login.php, /xmlrpc.php, password-reset actions, public REST API routes, contact and registration forms, search, comments, cart operations, coupon checks and payment-related callbacks. Custom plugins may add AJAX or REST actions that are easy to miss.
Your first priority should be the authentication surface. Use the controls in our WordPress login security guide—strong credentials, two-factor authentication and anomaly monitoring—then add throttling as a complementary layer rather than the only defense.
Rate limiting is not the same as blocking
A permanent block makes a binary decision. Rate limiting manages behavior over time. A policy can allow an initial burst, slow repeated activity, issue a browser challenge and temporarily reject only the requests that cross a threshold. This graduated response usually protects availability with less disruption to legitimate users.
Measure requests by more than one identifier. IP addresses are useful, but a corporate network may place hundreds of real users behind one address, while an attacker may rotate through thousands. Where privacy and architecture allow, combine IP reputation with account name, session, route, device signals and the action being attempted.
Put the cheapest control closest to the edge
A CDN or web application firewall can reject obvious floods before PHP, the database or WordPress plugins spend resources on them. Apply narrow rules to expensive and sensitive paths, and document exceptions for trusted integrations. Edge controls should preserve the real client address correctly so downstream logs and limits do not treat every request as the proxy.
Web-server and application controls provide more context. Nginx, Apache or a managed host can enforce request rates, while a security plugin or custom code can distinguish a failed login from a successful one. The strongest design uses layers: broad volumetric protection at the edge and action-aware decisions close to the application.
For API routes, pair limits with the authentication and permission checks described in our . Public read endpoints may tolerate higher volumes than authenticated write endpoints, exports or user enumeration.
Protect login and password recovery without enabling denial of service
Avoid long account lockouts triggered solely by failed passwords. An attacker who knows an employee's username could deliberately lock that person out. Prefer progressive delays, short temporary limits, risk-based challenges and alerts for repeated failures. Keep recovery usable, and test the policy with administrators who travel or use shared networks.
XML-RPC deserves a deliberate decision. If no application requires it, reduce exposure according to your hosting and plugin setup. If it is required, limit the methods and request patterns you actually use instead of applying a blanket rule that breaks publishing tools or integrations.
Review the tradeoffs in our before changing access, because legitimate services may still depend on the endpoint.
Rate-limit forms, search and commerce actions
Contact forms, registration, reviews and newsletter signups attract automated submissions. Add server-side validation, honeypots or challenges where appropriate, but also limit repeated submissions by action and session. Never rely on a browser-only control: bots can call the underlying endpoint directly.
On WooCommerce sites, watch login, account creation, coupon testing, cart changes, stock checks and checkout. Aggressive limits can interrupt real shoppers, payment callbacks or inventory synchronization, so separate customer-facing actions from trusted machine-to-machine traffic and test with every payment and fulfillment provider.
Use our to connect rate limiting with payment, account, plugin and recovery controls across the store.
Design limits from evidence, not guesswork
Collect a baseline before enforcing strict thresholds. Measure normal requests per minute, burst size, failure rate, response time and the source of traffic for each protected action. Search crawlers, monitoring systems, office networks and mobile users can create patterns that look unusual without being malicious.
Begin in observation mode where possible. Log which requests would have been limited, review false positives, then enforce a conservative policy. Tune by route and user state. A short burst allowance with a lower sustained rate often serves humans better than a rigid request-per-minute ceiling.
Centralize the relevant events using the approach in our . Alert on sudden increases, many accounts targeted from one source, one account targeted from many sources, repeated 429 responses and changes to protection rules.
Return safe, useful responses
For an API, respond with HTTP 429 Too Many Requests when the client exceeds the policy. A Retry-After value can help well-behaved integrations recover without creating a retry storm. Keep error messages consistent and avoid revealing whether a particular username exists.
For browser traffic, a short challenge or delay may be more appropriate than a hard error. Preserve accessibility and provide a support path for legitimate users. Cache rules carefully so one client's limited response is never served to everyone.
Test failure modes and operational ownership
Test from a staging environment and simulate bursts across login, forms, APIs and checkout. Confirm that administrators, customers, webhooks, monitoring and scheduled jobs still work. Verify behavior when the CDN is bypassed, an origin address changes or the rate-limit service becomes unavailable.
Include rate-limit changes in the same controlled process as plugin and infrastructure updates. Our explains how to validate changes before they reach production.
Assign an owner for every rule. Record the protected path, identifiers, threshold logic, exceptions, review date and rollback method. Remove stale allowlists promptly. A control that nobody understands becomes a source of outages or an invisible gap.
A practical implementation checklist
Inventory high-risk endpoints; establish traffic baselines; apply edge protection first; add application-aware limits for sensitive actions; combine multiple signals; use progressive responses; monitor 429s and authentication anomalies; test integrations; document exceptions; and review the policy after major traffic or architecture changes.
If you want the controls reviewed against your hosting, plugins and business flows, our can turn this checklist into a tested, site-specific protection plan.
Frequently asked questions
What is WordPress rate limiting?
WordPress rate limiting controls how many requests a client, account or session may send to a sensitive action during a defined period. It can slow, challenge or temporarily reject excessive requests while allowing normal visitors to continue.
Does WordPress include a global rate limiter?
WordPress does not provide one universal global rate limit for every login, REST API route, form and commerce action. Protection is normally applied through a CDN or WAF, the web server, a security plugin, or custom controls for a specific endpoint.
Should I rate-limit by IP address only?
No. IP limits are useful but incomplete because offices, mobile networks and privacy services may share addresses, while botnets distribute attacks across many addresses. Strong policies combine IP signals with account, session, route and action context.
What should a WordPress site return when an API client exceeds a limit?
For HTTP APIs, 429 Too Many Requests is the standard response. Where practical, include a Retry-After value and a clear machine-readable error so legitimate integrations can pause and retry safely.